Web Portals Governance: Granular RBAC and Native Auditing for the University CIO
Granular RBAC by site and section, technical guardrails and native auditing: how the university CIO cuts shadow IT without slowing anyone down.
Key Takeaways
- RBAC by dimension, not all-or-nothing: Griddo combines permissions by site, section, page, field and language — not just fixed roles like a traditional CMS.
- The Design System as technical guardrails: an editor can't inject code or break the platform, only publish within components that are already validated.
- Measured evidence, not projected: 5 times less onboarding time and 73% fewer unauthorized changes, measured on the real activity log of 11 university instances.
The dilemma you already know
Every time a faculty asks for access to publish faster, you face the same tradeoff: open up permissions and take on the risk, or keep them locked down and take on the complaint. Most platforms only give you those two options.
The cost of the first is measurable in incidents. The cost of the second, you pay in shadow IT: the faculty that can’t wait stands up its own site on its own, outside your inventory, outside your patching, outside your radar — until it shows up in a security scan or, worse, a breach.
This article is about the third option: a permissions model granular enough that opening access doesn’t mean giving up control.
Granular RBAC: from “all or nothing” to permissions by dimension
Most traditional CMS platforms offer fixed, inflexible roles. WordPress, for example, offers five static roles (Administrator, Editor, Author, Contributor, Subscriber) with barely any granularity for the permission needs of a federated university.
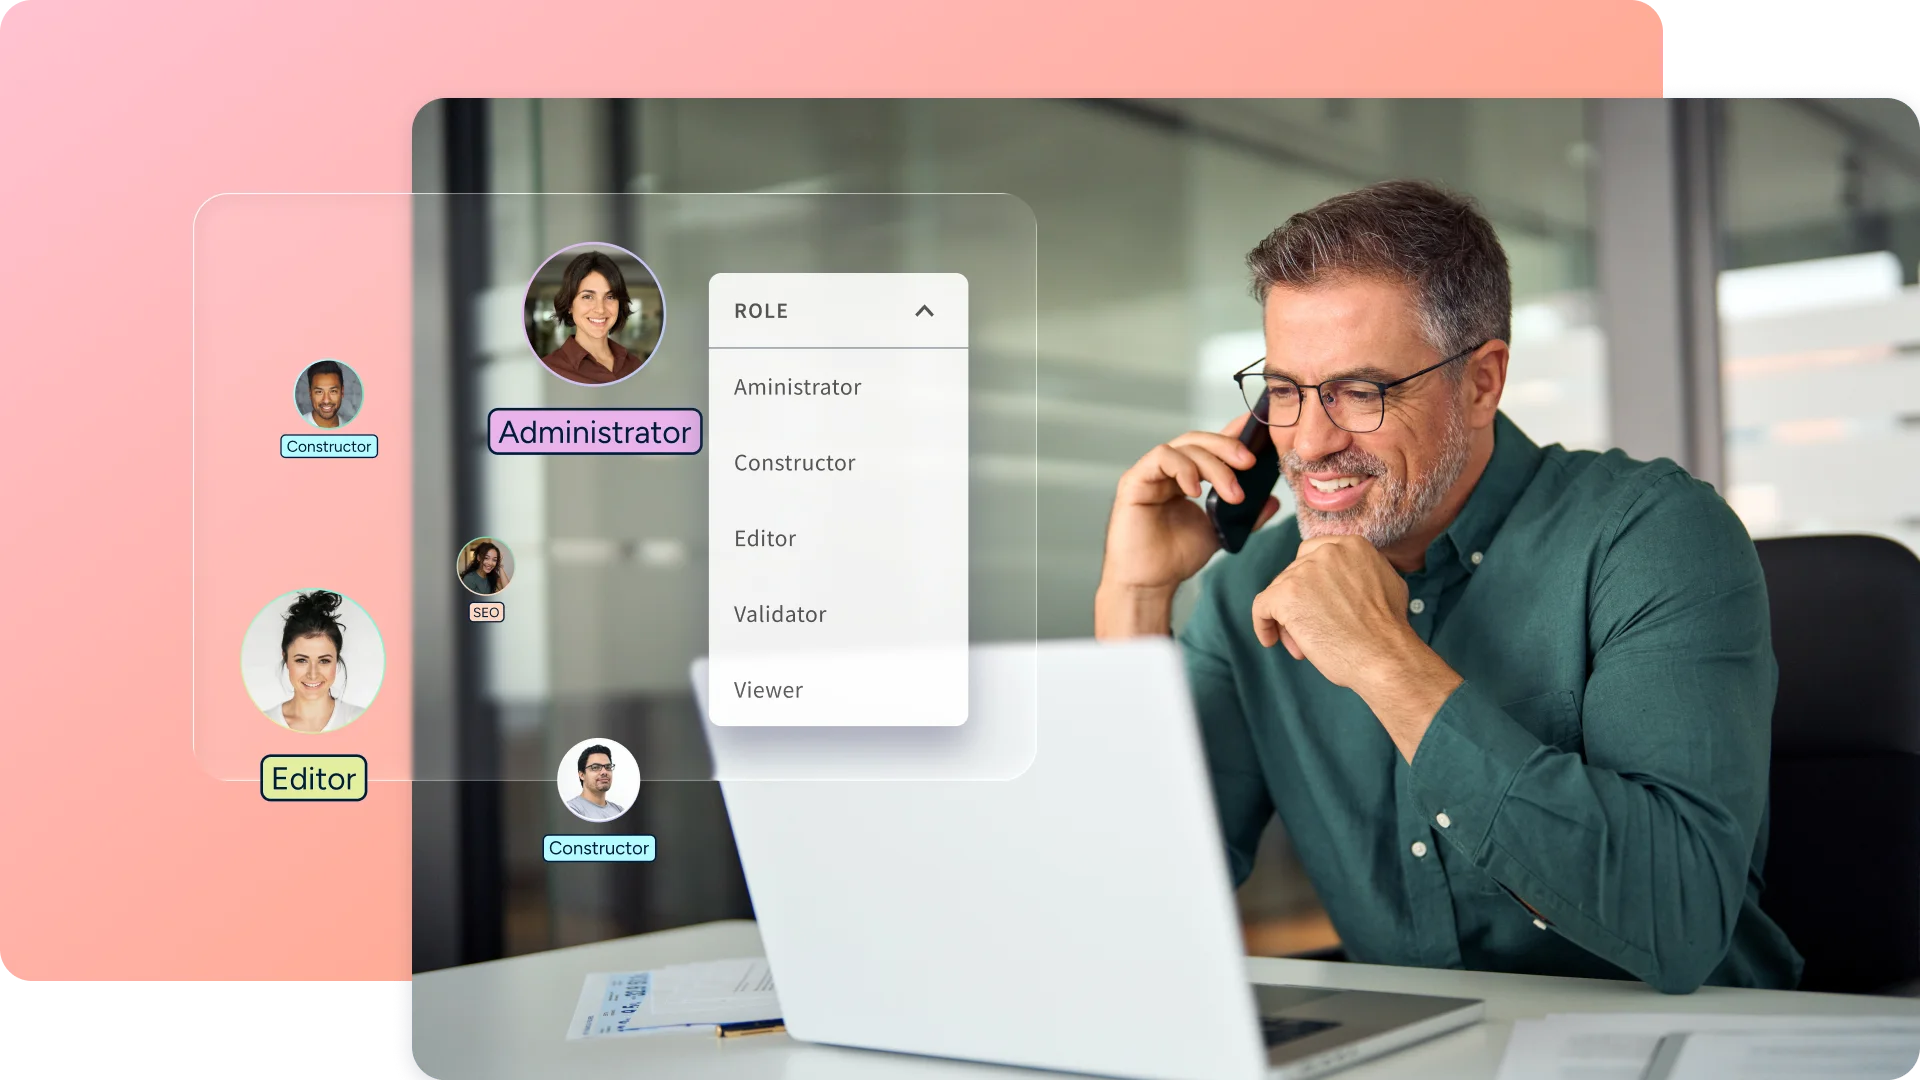
Griddo starts from 6 native roles (Super Admin, Administrator, Viewer, Webmaster, Editor, SEO Validator) and lets you create custom roles combining permissions by site, section, page, field and language. The difference isn’t how many roles exist by default, but how many dimensions of control you can combine:
| Control dimension | Traditional CMS | Griddo RBAC |
|---|---|---|
| Roles | Fixed, defined by the core | 6 native + custom roles |
| Permission scope | Whole site, or nothing | Site · section · page · field |
| Language | No native restriction | Native per-language restriction |
| Editorial flow | Draft / published | Multi-level: draft → review → publish |
| API tokens | Full access or none | Scope bounded by role |
| Auditing | Requires external plugin | Native, over 100% of actions |
This isn’t theoretical. At Universidad Pontificia Comillas, 60 people from 31 departments, faculties, institutes and chairs —Library, Alumni, ICAI, ICADE, OTRI, International Relations, the Refugee Program, the Energy Transition and Family chairs, among others— publish on a single instance without losing centralized governance. All six role variants, including the optional ones (Webmaster, Editor, SEO Validator), are active in production: the model is used exactly as designed, not collapsed into “everyone is an admin.”
We covered the underlying CIO challenge in depth in how to manage dozens of university websites without losing control; here the focus is the specific permissions model that supports that management.
The Design System as technical guardrails, not just brand ones
The Embedded Design System is, beyond a visual consistency tool, a security barrier. An editor works with predefined, already-validated components — they can change text, images and configuration, but can’t inject HTML, JavaScript or any code that runs at runtime. It eliminates, by the tool’s own design, the class of vulnerability that traditional WYSIWYG editors suffer from, not just the risk of an inconsistent brand. We already covered the security model of MACH architecture in detail in A university’s new security perimeter; here the focus is the guardrails at the editor level, not the infrastructure level.
Auditing and compliance, not just brand governance
The same permissions system underpins regulatory compliance: SSO access (SAML, LDAP, Active Directory, OAuth), MFA, encryption in transit and at rest, GDPR compliance by design, and an audit log covering 100% of actions on the platform — who published what, when and on which site, without relying on a third-party plugin. Griddo has passed the AWS Foundational Technical Review (AWS Qualified Software Partner), with its architecture evaluated on security, reliability, efficiency and operational excellence.
Measured on the platform itself: 5 times less onboarding time for a new editor and 73% fewer unauthorized content changes. Fewer after-hours incidents to put out, less time spent reconstructing who changed what.
The real cost of informal governance
Informal governance isn’t free, even though it never shows up on an invoice.
Industry analysts —Gartner and Everest Group, with estimates ranging from 30% to 50%+ of large enterprises’ IT spend— have spent years pointing out that a substantial share of technology in use runs outside formal control. A departmental website spun up without going through your inventory is exactly that pattern, applied to the domain that exposes the institution most to the public.
The education sector isn’t a bystander: IBM puts the average cost of a data breach in education at $3.7 million, and Comparitech already calculated an aggregate cost of $6.62 billion in ransomware attacks on US educational institutions back in 2020. Every forgotten microsite, every installation that stopped receiving patches because no one claims it, is one more candidate for that statistic.
Evidence in production, measured and auditable
The numbers above describe the risk. These describe what happens when the model works, measured directly on Griddo’s activity log — not a survey, not a projection:
- Universidad Europea runs five separate instances —IPAM (Porto), IADE Portugal (Lisbon), IADE Spain (Madrid), UDDI and Centro de Estudios Garrigues— with only 16 people, 7 of whom work across two or three instances in the same week. Adding a brand, a school or a country doesn’t require adding a technical team.
- Centro de Estudios Garrigues and Universidad Europea co-manage a single instance with differentiated permissions: each organization publishes its own catalog with no intermediaries or tickets between them.
- IE University combines three external digital agency profiles with seventeen internal accounts on the same instance: the agency runs the catalog and publishing volume, the internal team runs modules, page architecture and images. Neither blocks the other, and neither needs to go through you to do their part — which is, in the end, the point of good RBAC: that you stop being the mandatory middleman for every change.
How to talk about this with your CMO and your Communications lead
What’s coming
Griddo has page-level permissions on the roadmap for external or team reviewers (Soaring Spruce release, upcoming) — built to grant one-off review access without opening up the rest of the site. It isn’t generally available yet; we mention it here because it’s the same direction this article argues for: permissions that keep getting finer, never more binary.
Model limitations
Where this fits
This article is part of Griddo Journal’s Governance cluster.
Back to the Hub: Centralize Without Suffocating →
If you’re a CMO, start here → — why this same model accelerates your campaigns instead of slowing them down.
If you lead Communications, start here → — publishing speed for a distributed team, without losing institutional consistency.
Your next step
If you want to see this permissions model applied to your own map of faculties and campuses, let’s talk.